Sherlock secures the systems you build and operate onchain.
Your institution can deploy and manage capital in new ways onchain.
Doing so exposes that capital to code you do not control.
Sherlock builds the security program around that risk, from design through live operation.
A single exploit can drain an entire onchain position in seconds.
Moving capital onchain introduces risks your existing controls may not cover. Code can move assets through systems outside your control, causing irreversible loss before you can intervene.
Three failure modes that expose capital
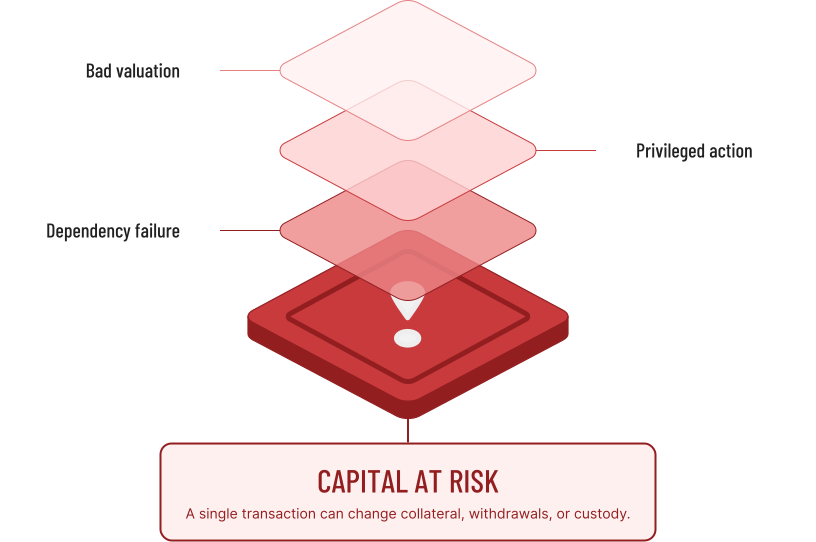
Who can move or stop capital?
Signers, approvals, exceptions, and emergency authority.
What if the price
is wrong?
NAV, oracles, stale or unavailable inputs.
Which dependencies change risk?
Protocols, markets, configuration, liquidity, and custody.
Who detects
and acts first?
Signals, decision rights, and approved response paths.
Sherlock builds and runs your onchain security program.
Your institution’s exposure spans its contracts, infrastructure dependencies, and the people authorized to move capital. Sherlock aggregates these layers into one security program, from architecture through live operation.
One engagement, from architecture review to live response
Your onchain
architecture
Contracts, signers, pricing inputs, and integrations define where capital moves and who can move it.

Prevent
Threat modeling shapes controls; private audits review contracts and configuration.

Detect
Live monitoring tracks permissions, pricing inputs, and critical dependencies.

Respond
Sherlock investigates alerts and coordinates institution-approved response.
Scope the onchain security program your institution needs.
Tell us what your institution is evaluating, building, or operating. We will identify the immediate risks and recommend where to begin.


We already secure the infrastructure your products depend on.
Sherlock secures the infrastructure that moves and manages capital onchain. We bring that firsthand experience to the financial products institutions build and operate.

34 engagements
Vaults V2 audit: 24 issues identified and fixes verified. Sherlock’s wider work spans vault design, releases, and integrations.

11 engagements
Sherlock’s V3 and V4 work includes private audits, a six-week public contest, and a live V4 bug bounty.
Active TVL across DeFi protocols Sherlock supports.
Audits and security reviews
Sherlock’s security services for institutional onchain products, before and after launch.
Purpose-built for institutional capital. Sherlock’s services work together around your institution’s architecture, operational requirements, and capital at risk.

Map how fund flows, privileged roles, and dependencies could put capital at risk. Rank the loss paths and specify controls before launch.
Threat model, prioritized controls, decision register.

Review custom contracts, offchain integrations, and the configuration planned for launch. Recheck material code and parameter changes before they go live.
Written findings, configuration checks, change reviews.

Define signer roles, key controls, approval thresholds, and emergency authority. Train authorized operators and rehearse exceptional actions.
Signer design, runbooks, training and drill results.

Turn the threat model into tested alerts for valuation inputs, collateral, privileged changes, and dependencies. Tune routing and rules as conditions change.
Monitored conditions, alert routes, tested detections.

Agree who can classify, pause, or restrict the system before an incident. Sherlock investigates alerts and coordinates the onchain response with your incident lead.
Response plan, named owners, incident records.
A standing security team for the onchain systems your institution operates.
Your institution’s exposure changes as code & infrastructure evolve. Sherlock reviews material changes, monitors agreed risk conditions, and coordinates incident response with your team.
Your code changes
A release alters permissions or capital flows.
Protocol upgrade
A protocol your product uses changes.
Dependency failure
An oracle, bridge, or integration fails.

Managed Monitoring and Response:
Sherlock reviews changes, monitors agreed conditions, investigates alerts, and coordinates approved action.
Protect client capital.
Limit disruption when systems fail.
Sherlock links live monitoring to pre-approved action. When a change or incident threatens capital, your team has a defined path to contain exposure, limit disruption to investors, and restore normal service.


Client testimonials
Aave has always implemented industry-leading security standards. V4 is designed to bring trillions of dollars and millions of users onchain, so continuing to meet those standards was not negotiable. Sherlock’s collaborative audit provided a deep review from a specialized team, and the public contest that followed confirmed their work was effective.
Founder and CEO of Aave Labs
Rock solid security has always been a priority for Sky. Over time, it's become one of the defining features of the project. It only makes sense that the team would work with the market leader, Sherlock.
Founder of Sky
We chose Sherlock because we were intrigued by the value of having multiple independent security researchers collaborating together. Our favorite part was the collaborative environment and effective feedback cycle between our team and Sherlock, making it a very productive experience.
Ethereum Foundation
What Sherlock delivers and how we are assessed.
Built for institutional diligence and oversight. Sherlock provides the evidence your team needs to evaluate our work, assess our own security controls, and oversee your engagement.
Reviewable
outputs

Framework alignment

Independent
review
Team members previously worked at these organizations. Their logos do not imply Sherlock client relationships or endorsements.