What is Sherlock? An Explainer for Builders and Teams
Sherlock’s current security services for Web3 teams, including private audits, Audit Engine, and post-launch security programs.
Sherlock Research
Updated November 13, 2026
Sherlock offers Collaborative Audits and Audit Engine for code review, and runs bug bounty programs for ongoing disclosure. Teams can scope operational security separately around signing, access, and production workflows.
Updated Nov 28, 2025
Sherlock is the first complete lifecycle security provider for Web3 protocols.
Protecting code from development through live operations, Sherlock applies AI, human expertise, and incentive-aligned validation across an interconnected security model. Trusted by leading protocols and ecosystems, Sherlock is building the foundation needed for onchain systems to scale globally.
There comes a time in every team’s journey when a project is ready to launch or existing code is ready for a major upgrade. It’s a moment that carries excitement and weight: where decisions ripple out to users, communities, and investors who put their trust in the system. At this stage, security is what separates fragile experiments from resilient infrastructure built to last.
Most providers approach that moment with a point-in-time audit - an essential step, but one that only captures a snapshot in time. Sherlock was created to go further. Formed in 2021, Sherlock combines collaborative reviews with elite researchers, global contests that apply adversarial pressure, bug bounties to guard live code, and financial coverage that aligns incentives. Together, these elements form a backbone of trust that helps teams ship with confidence and scale securely.
How Sherlock Delivers Complete Lifecycle Security
Sherlock aligns the three stages every protocol moves through, development, auditing, and post-launch protection, into a single connected security model. Each stage produces information that the next stage uses, so the system doesn’t restart each time the code changes.
Development: use Audit Engine for scoped code reviews and triage findings before release.
Auditing: Sherlock scopes Collaborative Audits and Audit Engine engagements around the system under review.
Post-launch: Once deployed, the code is monitored through structured bug bounties and triage. Findings from live usage are captured, validated, and routed back into the development process. Coverage sits behind this layer, tying financial consequence to any missed vulnerability.
The critical property is that context persists. Insights from development inform the audit. Audit output determines where post-launch scrutiny is applied. Post-launch findings influence how the next version of the code is written.
Rather than treating these stages as separate engagements, Sherlock runs them as linked components of a single model. This is lifecycle security in its actual form: security work that retains its state as the protocol moves forward.
Audit Engine
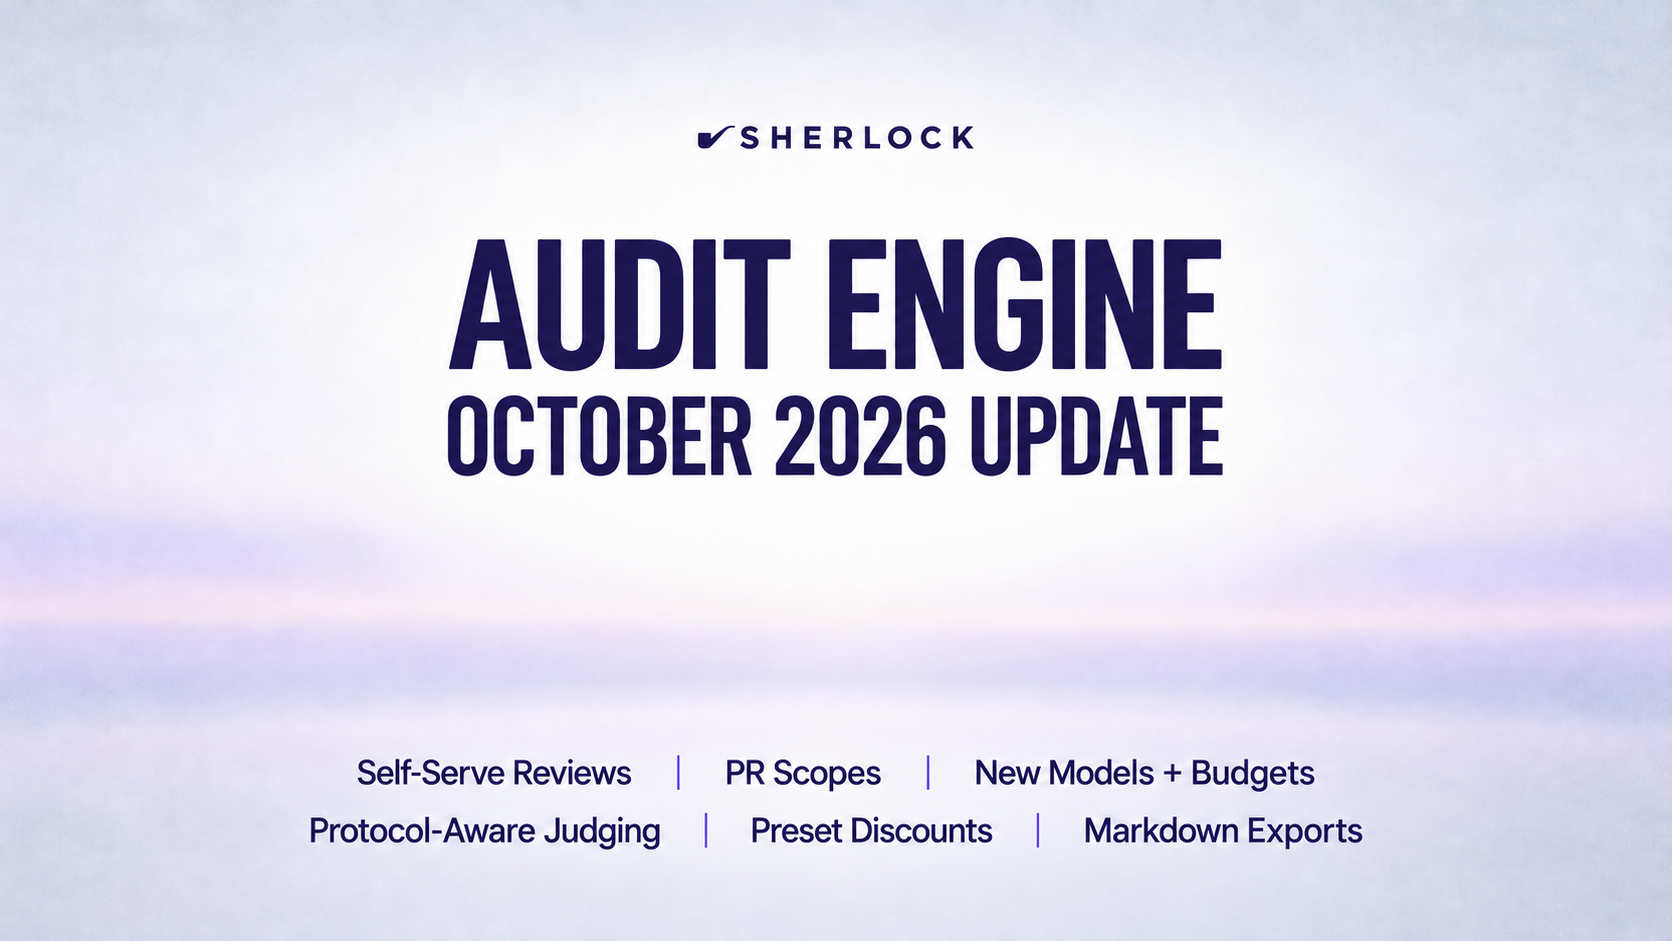
Audit Engine covers defined code scopes. Its release notes describe pull-request reviews and finding validation workflows.
Collaborative Audits
Sherlock’s collaborative audits are powered by data. Every researcher comes in with a performance profile built from contest history, past findings, and predictive modeling on the codebase in front of them. This actuarial approach lets Sherlock assemble the right team for each project, led by Senior Watsons whose results are proven across dozens of audits and contests. The process itself is hands-on: researchers work directly with your team, challenge design choices, and return to review fixes. Because incentives are tied directly to results - with most fees flowing to the auditors themselves - the outcome is deeper coverage, stronger remediation guidance, and code that enters production with measurable confidence.
Independent security reviews
Sherlock assembles specialist teams for Collaborative Audits based on the engagement’s scope and technical needs.
Bug Bounties
The bug bounty programs at Sherlock are designed to keep live code under constant scrutiny without overwhelming teams with noise. Proprietary validity checks and triage systems filter out duplicates and low-value submissions, distilling findings into a concise set of high-impact vulnerabilities. This structure saves developers significant time while ensuring meaningful issues are addressed quickly. Through tying bounties back to our audit model, Sherlock extends protection beyond deployment and keeps security active as protocols evolve.
Operational security
Operational security reviews focus on how access, signing, and release controls are managed around the protocol.
Who Sherlock Protects
Sherlock works with teams across the spectrum of onchain finance - from emerging projects preparing for their first launch to established networks securing billions in value. What unites them isn’t size, but responsibility: every protocol that touches user funds, coordinates validators, or underpins financial activity carries risk that must be secured. Sherlock’s model adapts to that reality, scaling protection to fit both growing startups and enterprise-grade infrastructure.
The platform secures:
- Layer 1 / Layer 2 upgrades — core protocol teams preparing or modifying network code and consensus-adjacent components.
- ZK privacy systems — protocols shipping proving/verification logic with tight correctness and performance constraints.
- Staking / restaking networks — operators coordinating validator sets and pooled collateral with slashing/exposure risk.
- Stablecoin issuers — teams managing collateralization, redemptions, and peg stability under real-time conditions.
- Lending / borrowing markets — money markets with oracle, liquidation, and interest-rate complexities.
- DEXs & derivatives venues — AMMs, orderbooks, and perps where small bugs can cascade across liquidity.
- Yield platforms & launchpads — vaults, routers, and orchestration layers aggregating user capital and upgrades.
- AI-driven / emerging primitives — novel mechanisms moving from research to production with changing attack surfaces.
Sherlock protects the protocols that carry the highest stakes in crypto: the systems where user trust, market stability, and billions in value are on the line.
Transcending the Point in Time Audit
Audits remain the foundation of protocol security - every serious team needs them, and Sherlock continues to treat them as a core pillar. But protocols don’t stop evolving once code is pushed live. Protocols grow, upgrades ship, and live systems face new attack surfaces every day. That’s why Sherlock built a platform that extends security across the full journey, making audits stronger by surrounding them with contests, bounties, and financial coverage.
The vision behind this model is to provide security that scales with the growth of onchain systems. Through aligning researchers, incentives, and capital, Sherlock creates trust strong enough to support the next wave of adoption. Our role is to transcend simply catching vulnerabilities - we aim to give builders the confidence to innovate and users the assurance that what they rely on is protected.
Conclusion
Sherlock helps teams review code before launch and plan for changes and reports once systems are live.
Ready to secure your protocol? Contact Sherlock’s security team today.